Validate detections
Execute a technique, generate telemetry, and confirm your rule fires before production traffic is the only test.
A technique emulation framework for blue teams and researchers. Generate telemetry, validate detections and observe tradecraft without hosted infrastructure or weaponised samples.

Combat Theater is a malware technique testing framework designed specifically for blue team detection engineers and security researchers.
It bridges the gap between blue teaming and malware development by giving defenders the ability to execute real-world malware techniques in isolation - safely, repeatably, and with full visibility.
No weaponised malware. No lab overhead. No infrastructure. Just accurate technique execution that behaves like the real thing.
Execute malware techniques, generate telemetry, validate detections effortlessly.
Experiment with advanced and niche tradecraft without hours of tedious development.
Atomic scripts, C2 frameworks and BAS platforms each solve a different job. Combat Theater is for isolating, customizing and observing malware techniques whether you're validating detections, purple teaming, or researching tradecraft.
| Combat Theater | Atomic Red Team | Caldera | BAS | |
|---|---|---|---|---|
| Ground-truth API-level execution logging | ||||
| No-code low-level API / memory customization | ||||
| Research-grade malware technique fidelity | ||||
| No hosting or web infrastructure required | ||||
| Threat playbooks / scenario chaining | ||||
| Run-safe payloads out of the box | ||||
| Easy install — up and running in 30 seconds | ||||
| Scriptable / extensible techniques |
One framework for the jobs that need real malware techniques, without C2 overhead or script-only approximations.
Execute a technique, generate telemetry, and confirm your rule fires before production traffic is the only test.
Independently validate how an EDR or detection stack actually performs against real techniques, before you buy, renew, or expand coverage.
Emulate real TTPs with clean, observable execution. Useful for joint red/blue work without standing up a full C2 stack.
Explore niche tradecraft or walk analysts through behaviors that matter, repeatably, safely, and with ground-truth logs.
A complete ecosystem for malware technique execution and validation.
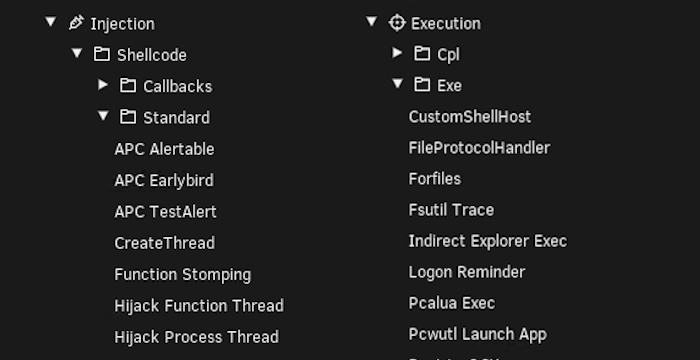
From commodity malware behavior to nation-state tradecraft — constantly updated for the current threat landscape.
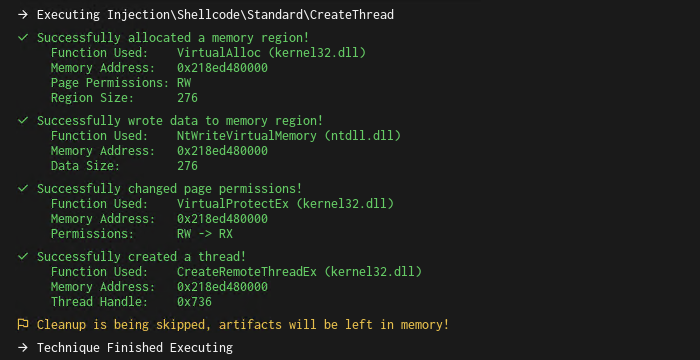
Ground-truth API, memory, and system interaction logs from the execution engine.
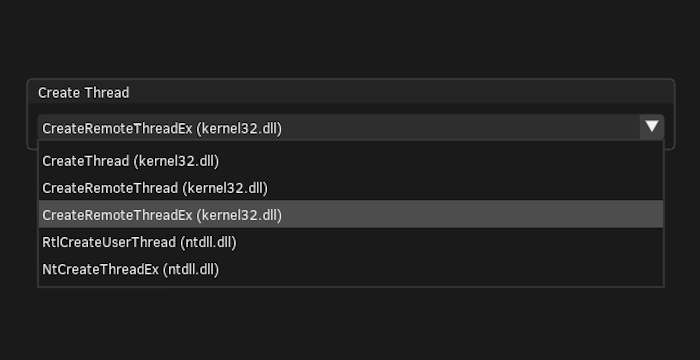
No-code pick'n'mix for APIs, page permissions, and execution options.
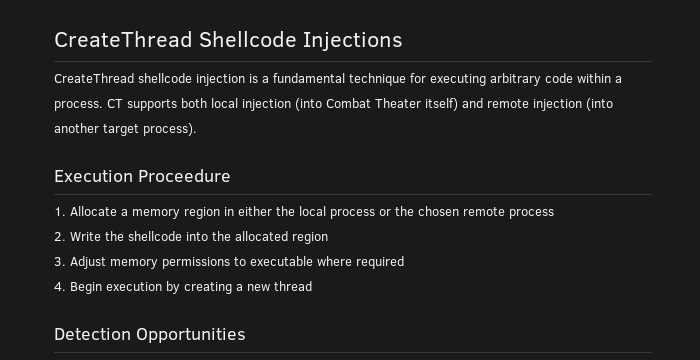
Execution flow, system interactions, and detection opportunities for defenders.
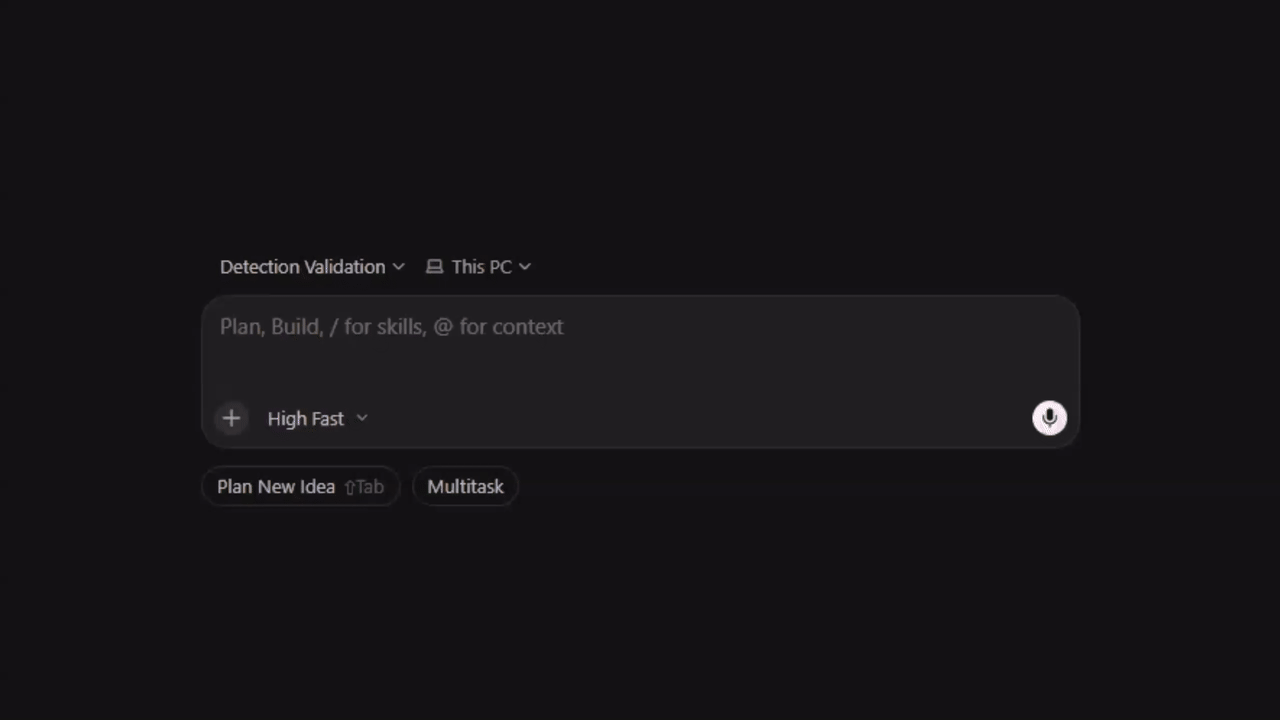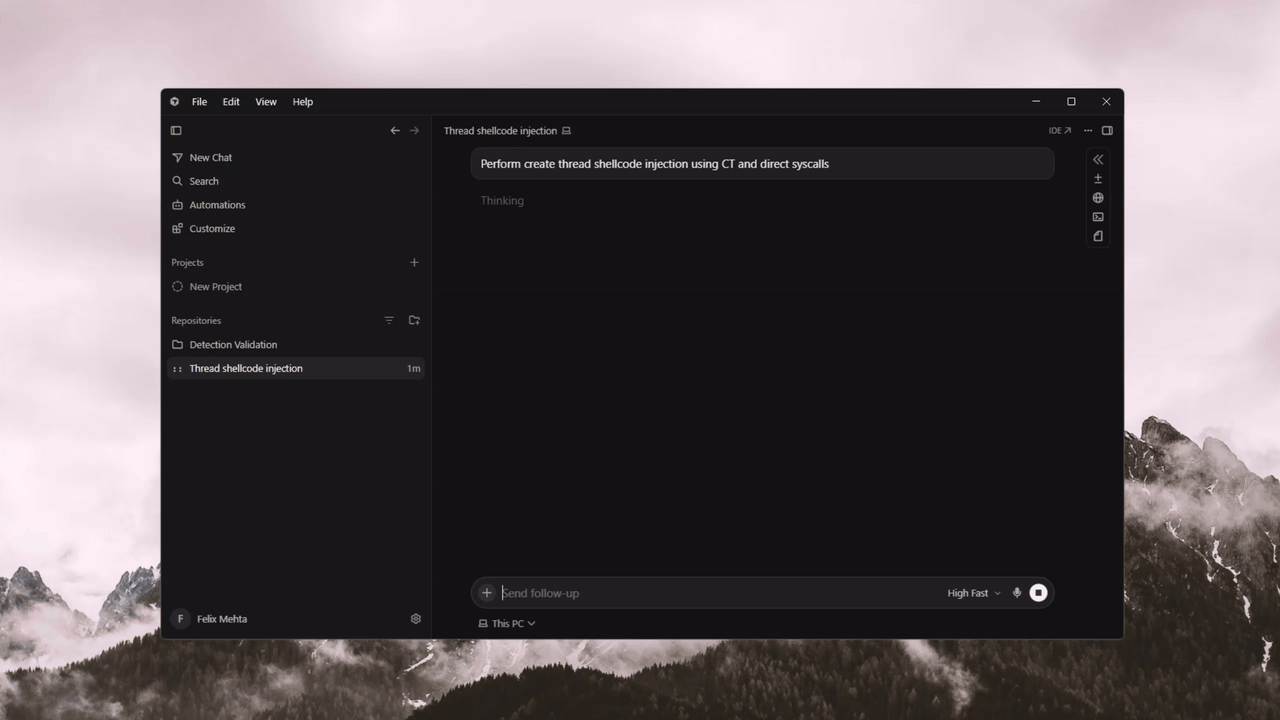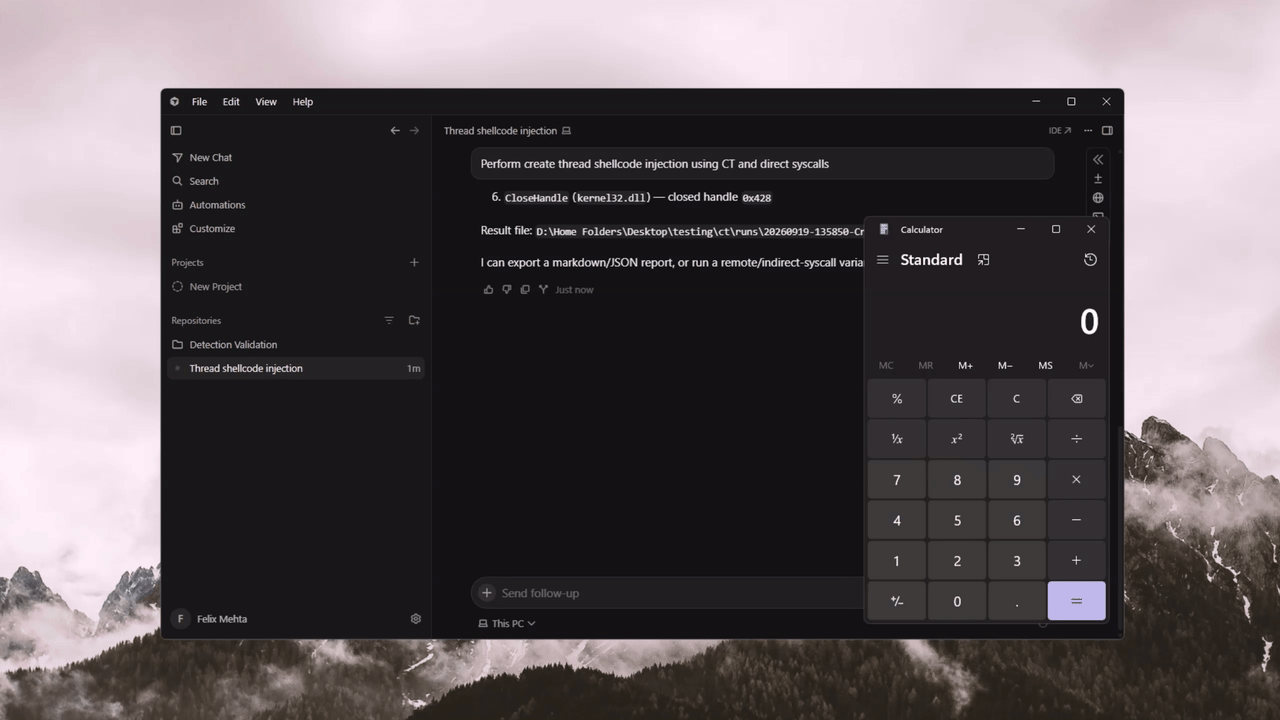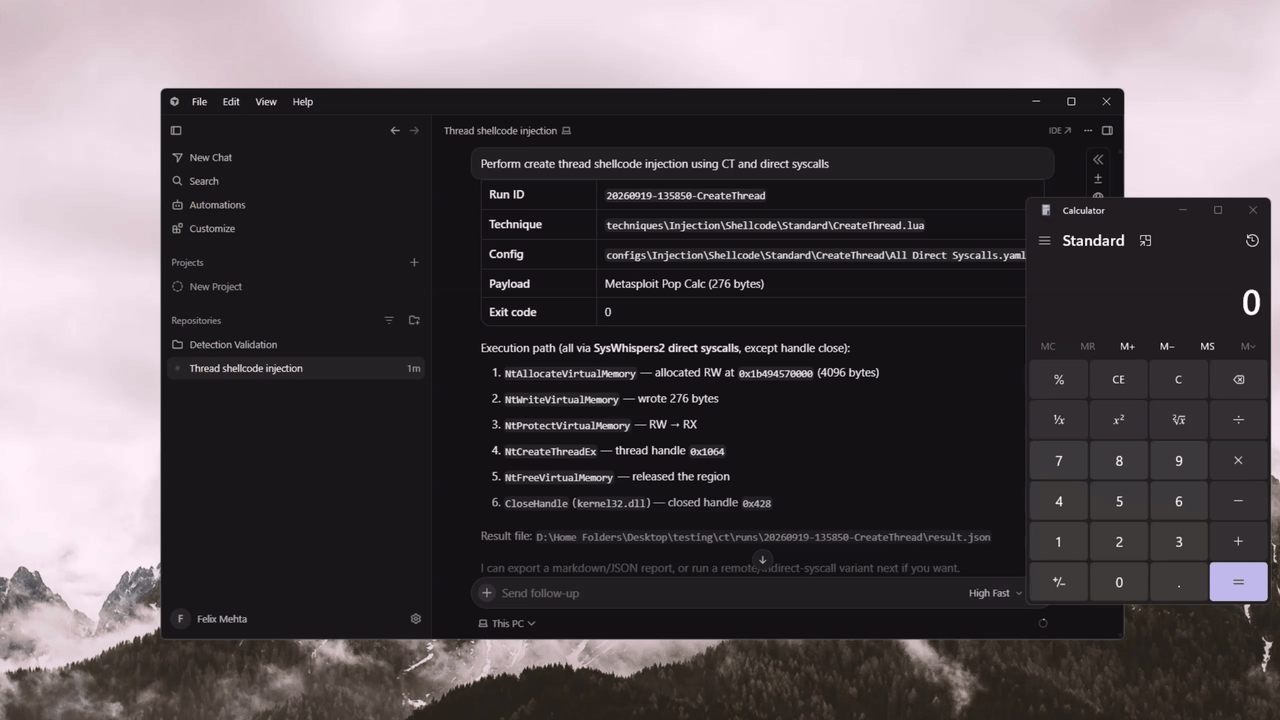
Connect over MCP and let your agent run techniques, launch playbooks, build configs, and author new techniques — without leaving the chat.
Execute continuously with confidence. Combat Theater uses custom built payloads designed to mimic real malware structure without the malicious side effects.
Our "run safe" payloads perform no network connections and no destructive actions — so you can execute continuously without collateral risk.
Shellcode, DLLs, EXEs, and more exotic formats out of the box.
Every payload ships with its source. Edit it, rebuild it, or duplicate it into your own variant.
Import real-world samples or custom payloads — the framework stays agnostic.
Sequence multiple techniques into a single execution flow. Build your own with the playbook builder or run a pre-curated chain in one click.
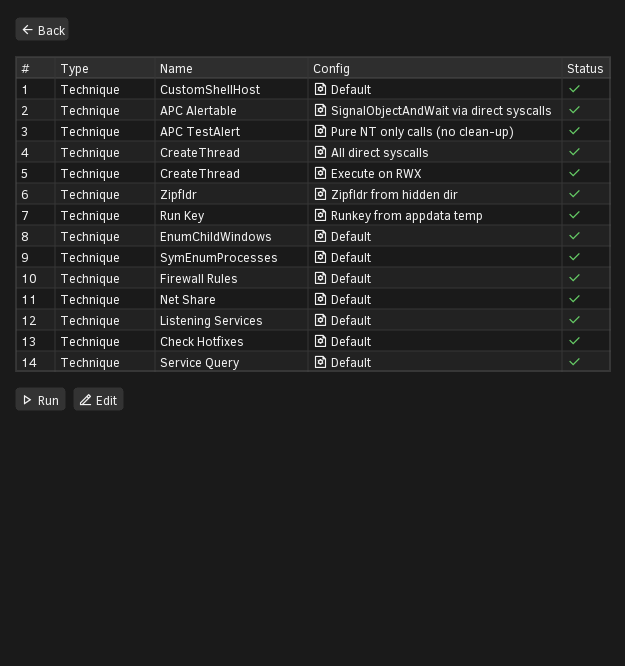
Emulate known nation-state tradecraft and advanced persistent threat chains.
Reproduce ransomware group activity and commodity malware behaviour.
Curated detection challenges — from easy wins to obscure, hard-to-catch techniques.
We provide 190+ ready to go technique scripts, however should you want to add your own or customize existing techniques, we expose our custom "ctapi" for you.
Combat Theater uses Lua as a control and orchestration layer, while all technique execution is performed by a native C++ engine.
Lua defines the GUI, configuration and execution flow of a technique but the underlying behavior is handled entirely by C++. This ensures techniques behave like real malware but with the ease of scripting.
-- CreateRemoteThread Shellcode Injection

local meta = require "meta"
local gui  = require "gui"
local api  = require "api"

function Init()
	meta.SetRequiredPermissions("user")
	meta.SetSupportedPayloads("shellcode")
	meta.SetReadme(readme)
end

function Configurator()
	gui.SetTarget(ctxTarget, true, true, true, false)
	gui.SetPayload(ctxPayload);
	gui.AllocateMemory(ctxAlloc)
	gui.WriteMemory(ctxWrite)
	gui.ChangePagePermissions(ctxPage)
	gui.CreateThread(ctxThread)
	gui.FreeMemory(ctxFree)
end

function ExecuteTechnique()
	-- Init
	local hTargetProcess, hTargetThread = api.InitializeTarget(ctxTarget)

	-- Payload
	local pPayload, iPayloadSize = api.GetPayload(ctxPayload)

	-- Memory
	local pPayloadAddress = api.AllocateMemory(ctxAlloc, hTargetProcess, iPayloadSize)
	api.WriteMemory(ctxWrite, hTargetProcess, pPayloadAddress, pPayload, iPayloadSize)
	api.ChangePagePermissions(ctxPage, hTargetProcess, pPayloadAddress, iPayloadSize)

	-- Execute
	local hThread = api.CreateThread(ctxThread, hTargetProcess, pPayloadAddress, false)

	-- Cleanup
	api.FreeMemory(ctxFree, hTargetProcess, pPayloadAddress)
	api.FreePayload(pPayload)
	api.CloseHandles(ctxFree, hTargetProcess, hTargetThread, hThread)
end
Not a BAS platform.
A local tool.
Combat Theater runs entirely on your machine. No cloud agents, no hosted infrastructure, no outbound product telemetry — just emulation you control.
Unlike Breach & Attack Simulation platforms, Combat Theater isn't a hosted service with agents and orchestration. It's software you install and run locally.
Execute techniques on your workstation or lab VM with no cloud dependency. After install, it works without a network.
No infrastructure to provision. No agents to deploy. No dependencies to babysit. Install and go.
No technique execution logging or product usage telemetry sent outbound. Your runs stay where you ran them.